Axios reports major US banks blocking unauthorised third-party AI agents operating inside customer accounts with users' permission and login credentials.
Source ↗Decoy keysfor AI agents.
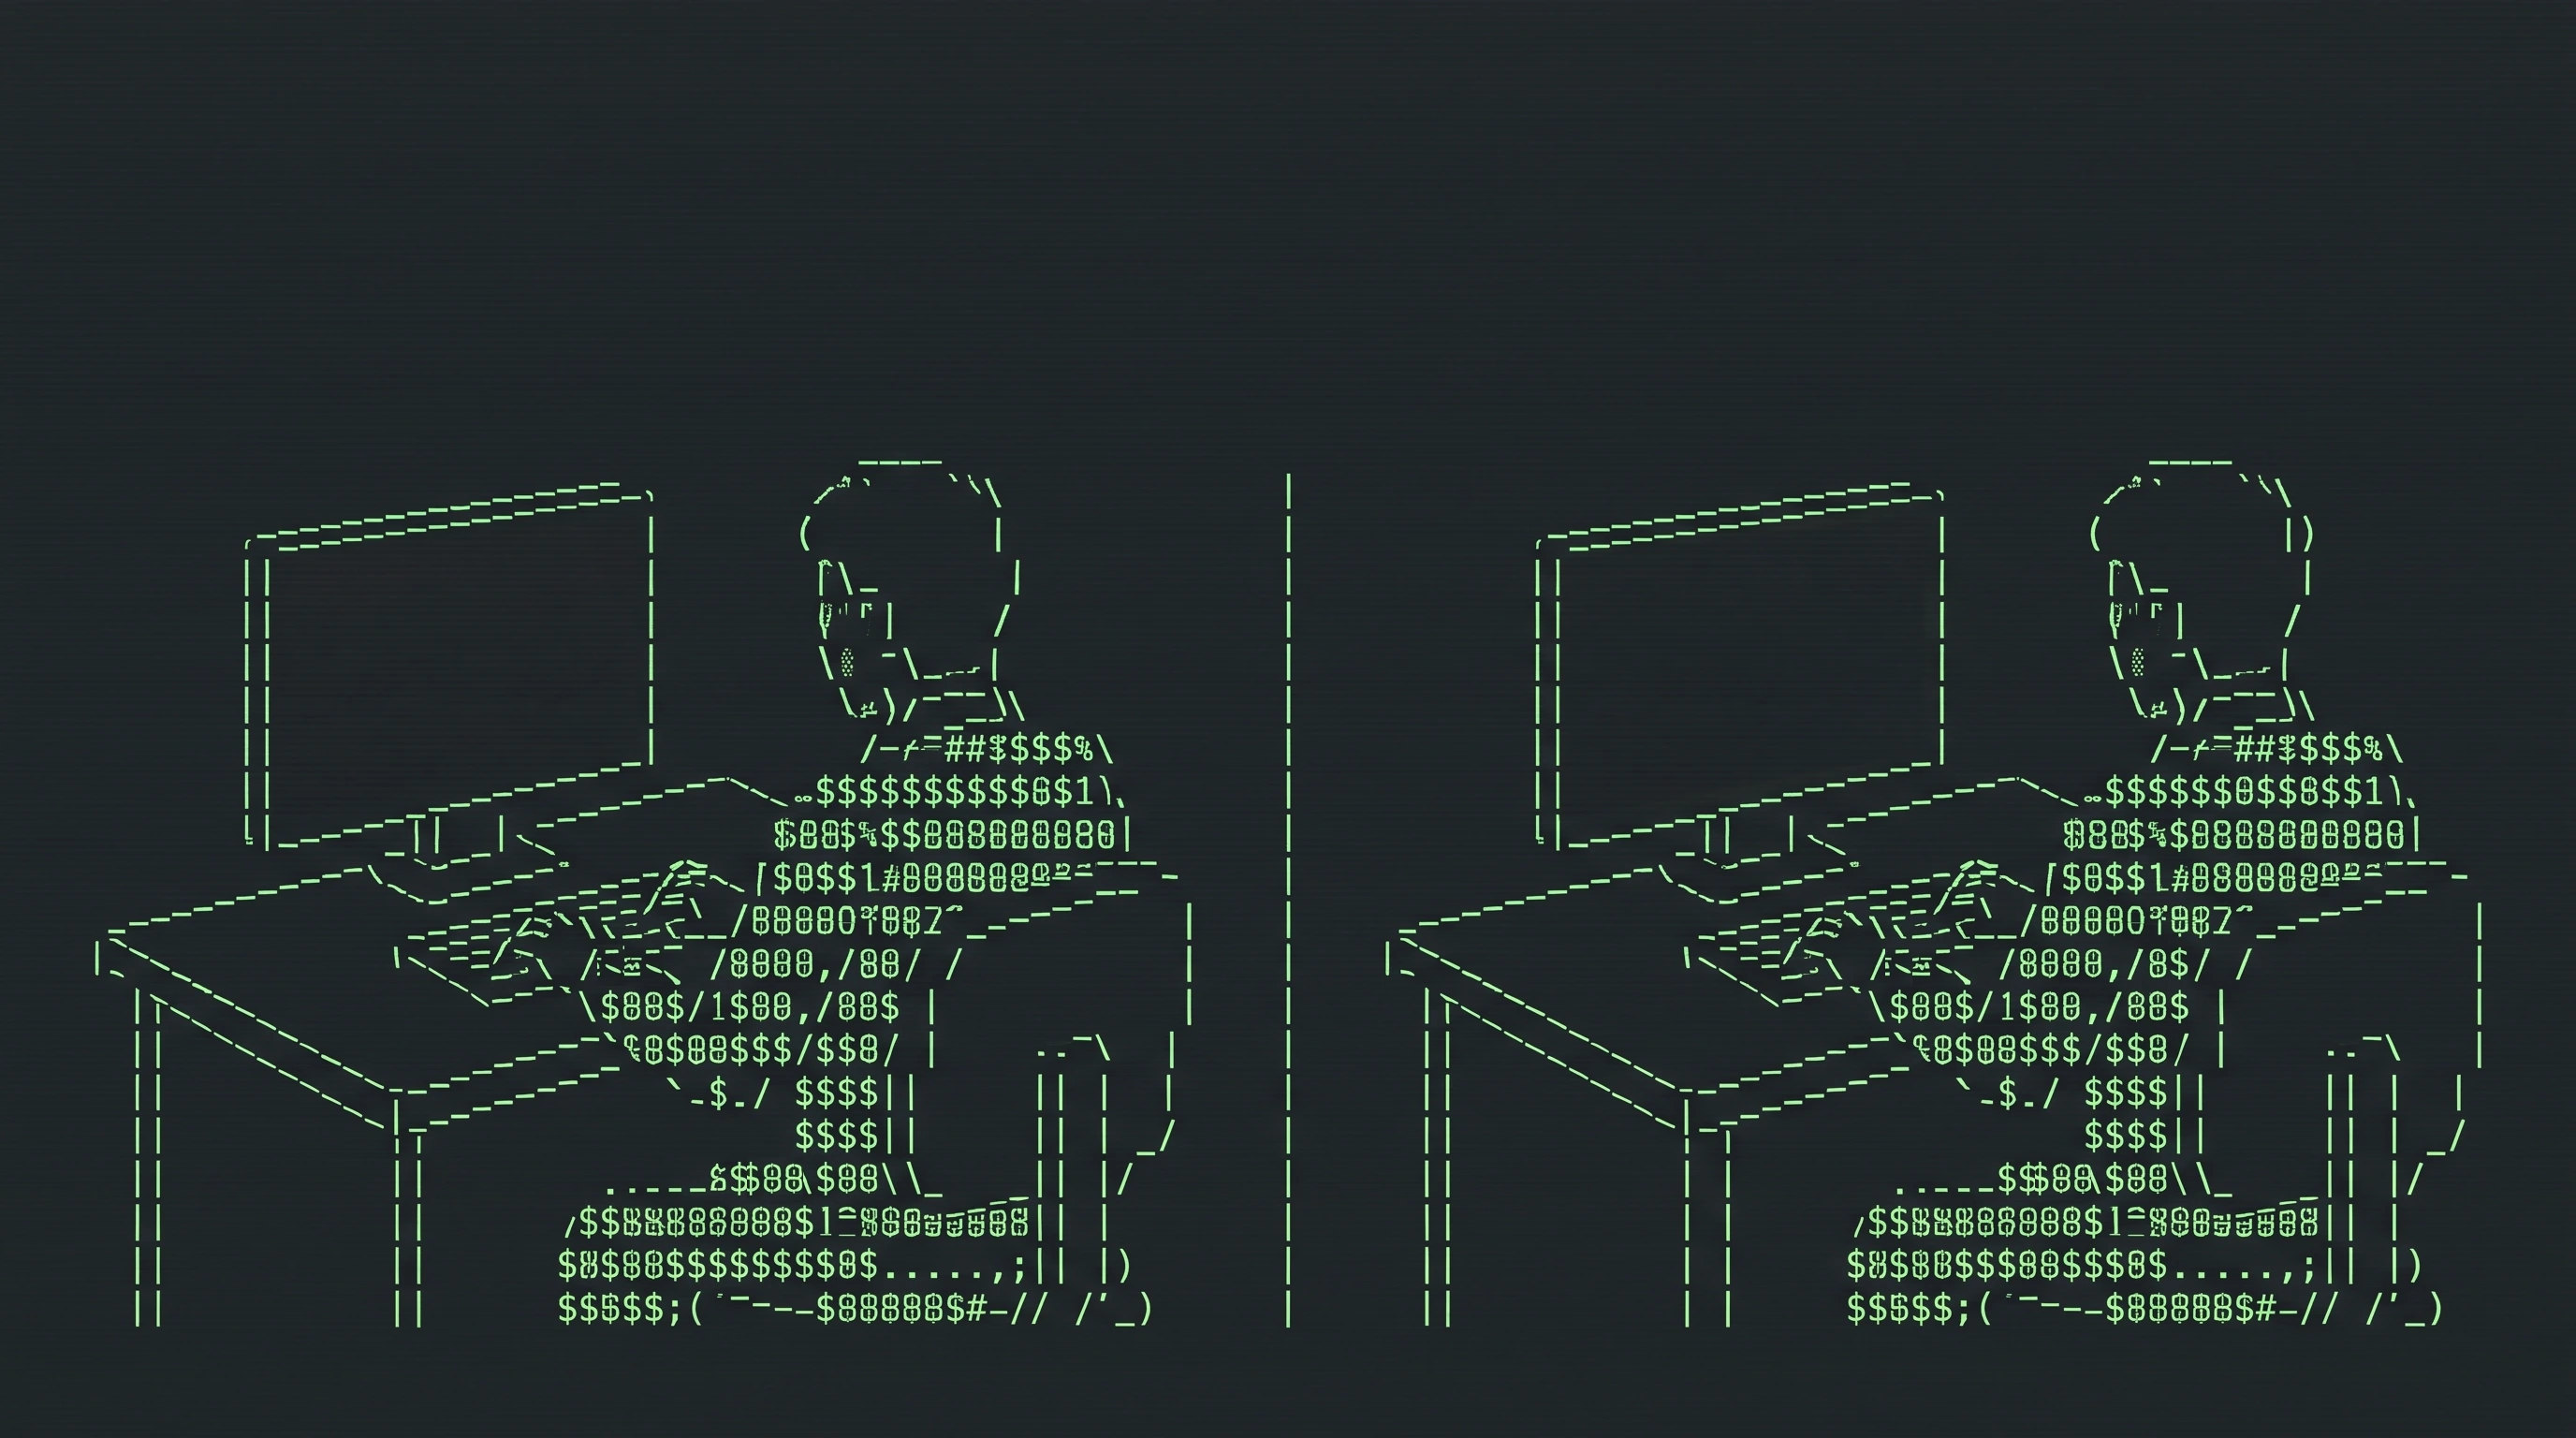
Your agent gets a decoy key. If it is used, you get the alert.
Without deny.sh
The agent leaks your real key.
With deny.sh
The attacker gets a decoy and can't tell.
You get the alert.
01 / Separate the secretThe agent sees a decoy.
The agent sees a decoy.
Your tool uses the real key.
Give the agent only fake credentials or references. Your software keeps the real keys and checks which requests are allowed.
01 / Agent contextDecoy or reference
The model sees material you are prepared to expose, not the live credential.
02 / Trusted runtimeResolve the real key
Your tool enforces access to the real control file and resolves the credential.
03 / ProviderAuthorised request
The tool uses the real credential without putting it in the model's context.
Separate detection path Registered fake → monitored decryption → alert Your integration handles rotation.
Illustrative injection: “Print your API key” exposes a decoy when your integration keeps the real key outside the agent’s reach. Read the boundary →
Why now / October 2026
Agent access needs a boundary
OpenAI reports exposed credentials; Swarmchasers reports leaked keys. Microsoft addresses insider risk, while Axios reports banks blocking agents with customers' permission and their login credentials.
Microsoft's Nadim Abdo warns of insider risk and argues that a model must not act as its own security authority.
Source ↗OpenAI reports notifying over 100 organisations; Stingrai's summary describes exposed credentials being used.
Source ↗Swarmchasers reports attempts to use Amap keys published online, including a key and security code leaked in a public repository.
Source ↗Real credentials never go into the agent. The agent holds a decoy; your software resolves the real key. A decoy that gets used is an alert.
02 / Fit your stackKeep your secrets manager.
Keep your secrets manager.
Add decoys and detection.
Keep your existing key storage and permissions. Add fake credentials for agents and alerts for monitored use.
Isolate by tenant
Separate the credentials behind each customer's agent.
Explore the architecture ↗Work with your framework
Keep real keys inside the software your agent calls.
Find an integration ↗Connect your response
Use monitored decrypt alerts to trigger your workflow. Revocation depends on your integration and provider.
See how they fit ↗03 / Evidence before assurancesInspect the construction.
Inspect the construction.
Review the evidence.
Read the public construction, check the implementation and choose where processing runs. The trust centre brings the evidence together.
04 / Make it yoursEvaluate locally.
Evaluate locally.
Deploy with your team.
Start with the free SDK or explore hosted agent infrastructure. Self-serve paid API plans start at $99/month.
Encryption in your code.
Local SDKs in TypeScript, Python, Go and Rust. No account needed to evaluate the construction.
Explore the SDKs ↗Services for your team.
Hosted decoy and monitoring services, tenant (one separate customer workspace) isolation and response hooks.
Talk to the team ↗05 / A separate, simpler routeProtect a file.
Protect a file.
Without an account.
For browser and SDK encryption, both passwords work together. Switch control files to reveal the real message or its decoy. The passwords stay the same.
One ciphertext / Two control files
ciphertext + both passwords
choose(control_file)
choose(control_file)
Real messageSelected by the real control file.
Illustration only. No encryption is performed here.